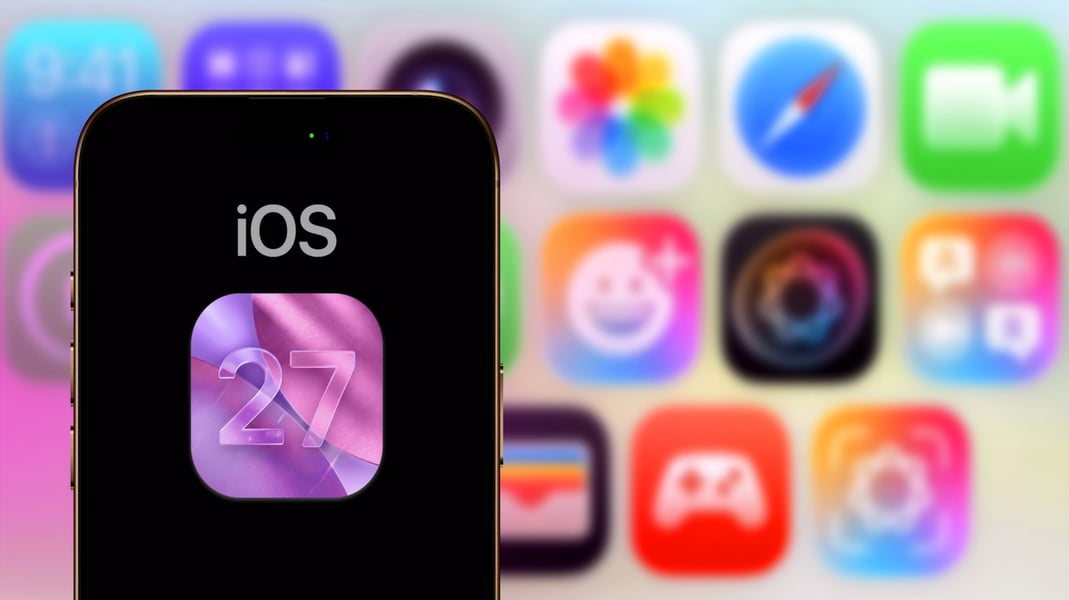
Apple released iOS 27.2.1 on November 9, fixing security flaws that could expose iMessage group conversations or allow unwanted wireless pairing on an iPhone. The update also includes general bug fixes, although Apple has not provided a separate list of those changes.
Two of the security fixes concern who can enter a group chat and which messages a new participant can see. Apple says one vulnerability could allow a remote attacker to join an iMessage group and receive its messages. Another could let someone added to a group access messages sent before they joined.
The release is a maintenance update, not a newly announced set of iPhone features. Its security bulletin lists nine vulnerabilities across seven component names, with separate entries for the two Messages flaws and two issues in CoreUtils.
Apple’s brief release note for iOS 27.2.1 says: “This update provides bug fixes and security updates for your iPhone.” The more detailed security bulletin explains the vulnerabilities addressed in both iOS 27.2.1 and iPadOS 27.2.1.
Those descriptions concern possible unauthorized access, not a finding that every group conversation was exposed. Apple’s bulletin does not say these flaws were exploited in attacks. That absence is not proof that exploitation never occurred; it is the limit of the company’s published disclosure.
Several other fixes address attacks that require proximity to the device. An AirPlay flaw could allow someone within Bluetooth range to bypass the limit on pairing-code attempts. A Bluetooth memory-management issue could let a nearby attacker corrupt process memory.
The two CoreUtils entries also concern pairing. One describes a malicious Bluetooth device establishing a pairing without user interaction. The other combines bypassing the pairing-code attempt limit with pairing without user interaction. Apple says it strengthened checks for the first issue and improved state management for the second.
A separate vulnerability in rapportd could let an attacker on the same network bypass the limit on AirPlay pairing-code attempts. The distinction matters: Apple describes the reach of these wireless issues differently from the remote iMessage group-chat flaw. The bulletin does not present every vulnerability as something an attacker can exploit from anywhere.
The remaining entries cover App Intents and the brotli compression component. Apple says an app could access sensitive user data through the App Intents authorization issue, while maliciously crafted input could cause memory corruption through brotli. The fixes use improved state management and input validation, respectively.
Apple lists the iPhone fixes as available for iPhone 11 and later. The companion iPadOS bulletin covers iPad Pro 12.9-inch fourth generation and later, iPad Pro 11-inch second generation and later, iPad Air fourth generation and later, iPad ninth generation and later, and iPad mini sixth generation and later.
The patch also sits on a different track from the iOS 27.3 developer beta previously covered by Eastern Herald. That report concerned software still in testing. The November 9 bulletin documents fixes in the released 27.2.1 versions, rather than treating beta features as part of this patch.
For iPhone owners, the clearest reason to pay attention is the security detail behind Apple’s one-line release note: group-chat access, message history and wireless pairing all receive fixes. The company has not identified which everyday glitches its general bug fixes address, and the release note offers no specific promise of better battery life or faster performance.